HIPAA Compliance For AWS
HIPAA compliance software for healthtech and software teams building on Amazon Web Services.
Managing HIPAA Compliance In AWS
The Health Insurance Portability and Accountability Act (HIPAA) dictates data privacy and security requirements for managing medical information. Healthcare organizations have to manage many security concerns when building HIPAA complaint solutions and managing protected health information (PHI) in Amazon Web Services (AWS). While AWS has developed several cloud security programs, and provides a business associates agreement (BAA), security and compliance is ultimately a shared responsibility for AWS and the cloud customer.
Under the AWS cloud shared responsibility model, AWS is responsible for many of the HIPAA physical safeguards, but it is up to the cloud customer to manage all administrative and technical safeguards. Organizations must adopt HIPAA administrative policies and implement HIPAA technical controls including backup and disaster recovery, audit logging, and intrusion detection.
Dash ComplyOps: HIPAA Compliance Automation for AWS
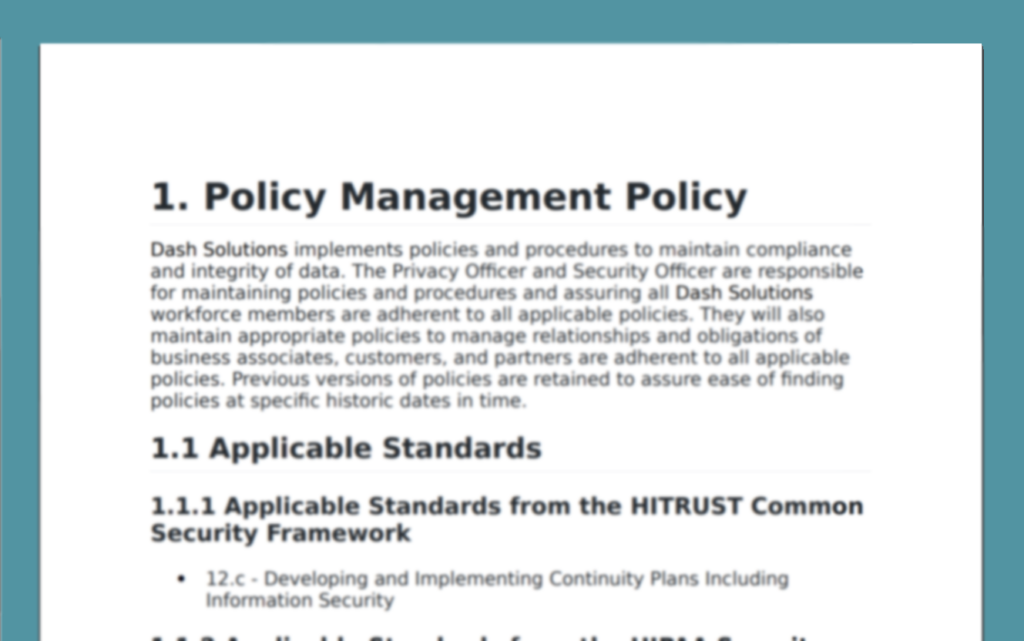
HIPAA Administrative Policies for AWS
HIPAA requires that organizations set administrative policies and address safeguards including creating compliance roles, performing risk assessments, and managing incident response. Dash enables teams to generate custom compliance policies based around on your organization’s needs, structure, and technologies. Policies are designed around Amazon Web Services and customized through easy to answer questions.
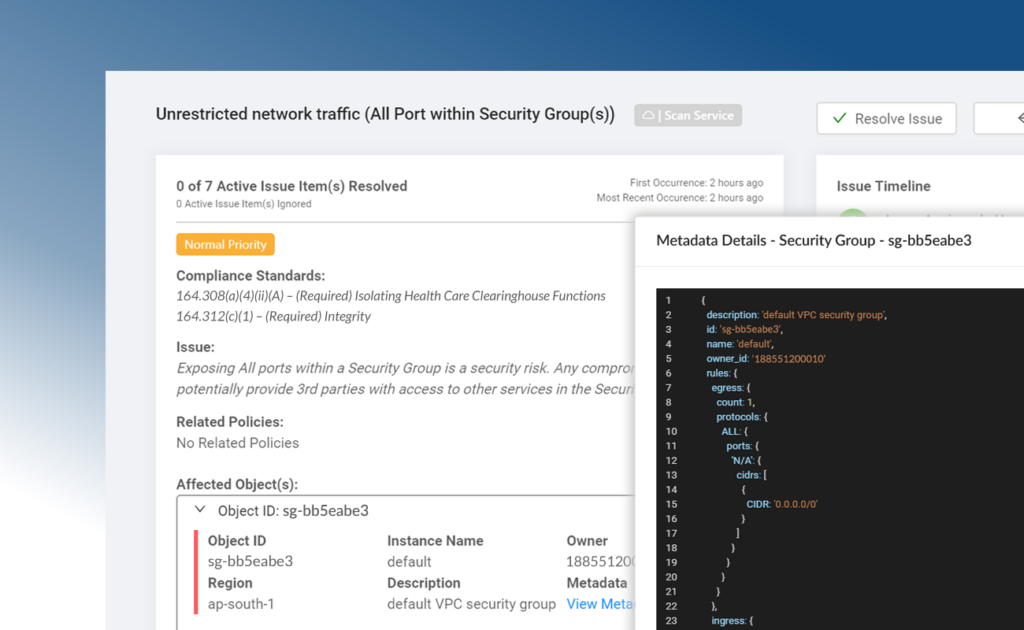
HIPAA Technical Safeguards for AWS Services
Dash ComplyOps establishes a set of HIPAA technical controls based around your organization’s established policies and procedures. Security controls are built around individual AWS cloud services, best security practices, and HIPAA/HITECH standards. Organization can utilize Dash to find and resolve compliance issues and maintain technical security standards.
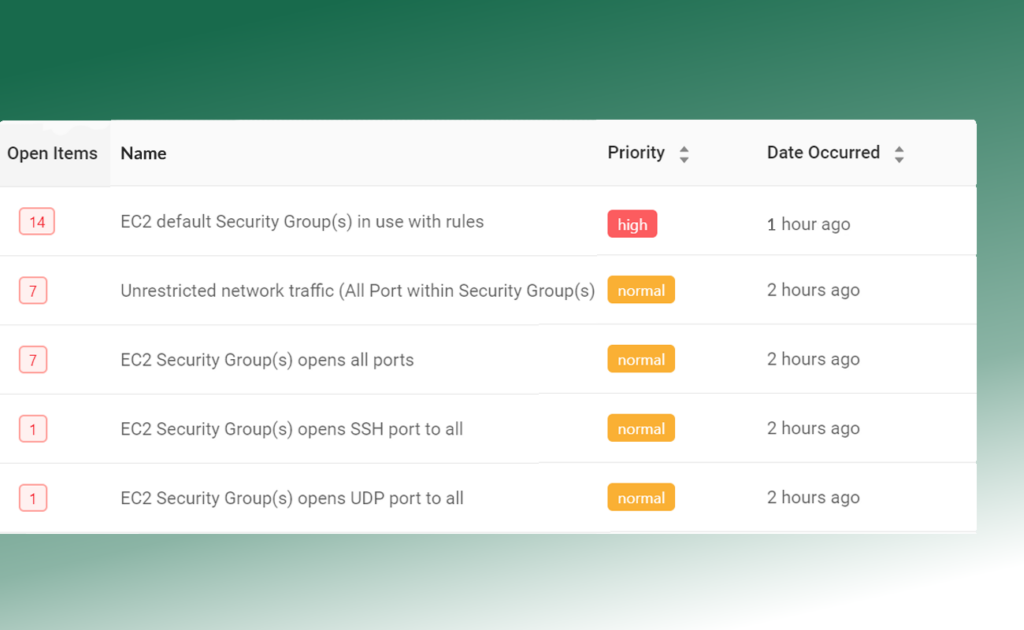
Continuous HIPAA Monitoring for AWS Accounts
Dash continuously monitors your AWS accounts for HIPAA configuration and security issues. Dash detects compliance concerns in your cloud environment such as unencrypted EBS volumes, audit logging issues and S3 buckets that are open to the public, alerts your team, and provides steps for resolving issues before they become full-blown violations.
Meet HIPAA Requirements On AWS
Dash ComplyOps enables teams to plan and implement compliance safeguards and security controls including the following
Security & Privacy Officer Roles
Designate Security and Privacy Officer roles and define HIPAA compliance responsibilities within the organization.
Workforce Training & PHI Access Policies
Create policies for managing HIPAA requirements related to employee training and system access. Dictate access to PHI and sensitive data.
Audit Logging for PHI
Configure an audit logging solution and determine how logs are collected, reviewed, and accessed to meet HIPAA requirements.
Intrusion Detection
Implement and perform intrusion detection. Find malicious behavior and compliance issues before they become violations.
HIPAA Risk Assessment & Review
Address HIPAA risk assessment and risk analysis requirements. Set review periods for gathering compliance information, reviewing safeguards, and handling reports.
Incident Response & Breach Notification
Create a standard operating procedure for responding to security incidents. Set policies for notifying customers and vendors of potential HIPAA security breaches.
Backup & Disaster Recovery
Setup a Disaster Recovery team and set Recovery Time Objectives (RTOs) for responding to application and service availability issues within your organization.
PHI Encryption In Transit & At Rest
Set standard policies and technical controls for encrypting PHI data in-transit and at-rest on AWS.
From healthcare providers to software services and medical devices. You’re in good company.
Trusted by Healthcare and Healthtech Teams
HIPAA Security Rule Standards Covered By Dash Controls
Dash ComplyOps provides compliance controls built around cloud computing and HIPAA safeguards including
Encryption and Decryption (164.312(a)(2)(iv))
Ensure that all cloud data volumes, cloud databases, and transmitted data is encrypted.
Protection from Malicious Software (164.308(a)(7)(i))
Ensure that cloud network and security groups do not expose ports or access that may compromise PHI.
Information Access Management (164.308(a)(4)(i))
Ensure that your company uses proper user roles and policies in AWS. Avoid HIPAA violations stemmed from access issues.
Audit Controls (164.312(b))
Ensure that your organization’s logs are properly collected, aggregated, and analyzed.
Risk Analysis (164.308(a)(1)(ii)(A))
Set procedures for conducting risk assessments. Receive alerts and notifications for remediating compliance issues.
Facility Access Controls (164.310(a)(1))
Address physical security requirements utilizing Amazon Web Services safeguards provided under BAA.
HIPAA Compliance Software Built for AWS
Dash ComplyOps enables organizations to build a robust HIPAA security plan and security controls for Amazon Web Services
Designed for AWS-Native Healthtech Teams
Policies, monitoring, and technical controls designed for AWS-focused and cloud native healthtech teams.
Works Alongside 100+ AWS Services
Dash can be used alongside the hundreds of AWS cloud services to rapidly build, manage and get-to-market.
Automate HIPAA Compliance on AWS
Build and Automate Your HIPAA Compliance Program for Amazon Web Services